Answer a few questions — you see whether NIS2 applies to your company, without giving contact details.
NIS2 compliance in Malta — clarity in three minutes
NIS2 documents for 24 countries — based on each country's own law
Start the test Your first NIS2 document: the risk management policy
NIS2 Magic Button From your company's website address to a pre-filled NIS2 profile — you confirm only what is missing.
A company-specific risk management policy based on your country's law — one-time payment, comes with an account and a living documentation profile. 129 EUR
All prices are net (excluding VAT). Invoices are issued by AIPOS OÜ (Estonia).
The path: free check → your first document (the risk management policy) → the full documentation package.
Delivery: typically 60 minutes. If the quality gate requires additional review, we will notify you by email.
- What: a platform that produces NIS2 documents from your company profile and checks each of them against the national law.
- For whom: companies that fall under the national NIS2 act, and suppliers whose customers ask for NIS2 evidence.
- How: profile → document → three-stage check → download.
Straight from the law
4. (1) For the purposes of this order, the following entities shall be considered to be essential entities: (a) entities of a type indicated in the First Schedule which exceed the ceilings for medium-sized enterprises provided for in accordance with Article 2(1) of the Annex to the Commission Recommendation 2003/361/EC; (b) qualified trust service providers and top-level domain name registries as well as DNS service providers, regardless of their size; (c) providers of public electronic communications networks or of publicly available electronic communications services which qualify as medium-sized enterprises in accordance with Article 2 of the Annex to the Commissioner Recommendation 2003/361/EC; (d) public administration entities mentioned in article 3(3)(f)(i); (e) any other entity of a type referred to in the First or Second Schedule that are identified by the CIP Department or where designated the competent authority as an essential entity pursuant to articles 3(3)(b) to (e); (f) entities identified as critical entities under the Resilience of Critical Entities and Infrastructures (Identification, Designation and Protection) Order in article 3(4); (g) entities which the CIP Department or where designated the competent authority identified before 16 January 2023 as operators of essential services in conformity with: (i) Directive (EU) 2022/2555 of the European Parliament and of the Council of 14 December 2022 on measures for a high common level of cybersecurity across the Union, amending Regulation (EU) No 910/2014 and Directive (EU) 2018/1972, and repealing Directive (EU) 2016/1148 (NIS 2 Directive); or (ii) national law. (2) For the purposes of this order, entities of a type referred to in the First or Second Schedule which do not qualify as essential entities pursuant to sub-article (1) shall be considered to be important entities. This includes entities identified by the CIP Department or where designated the competent authority as important entities pursuant to articles 3(3)(b) to (e). PART II – ENFORCEMENT COMMITTEE, CRITICAL INFRASTRUCTURE PROTECTION DEPARTMENT AND CSIRTs
S.L. 460.41 article 4
The text is from the country's official, enacted law — verbatim, not paraphrased.
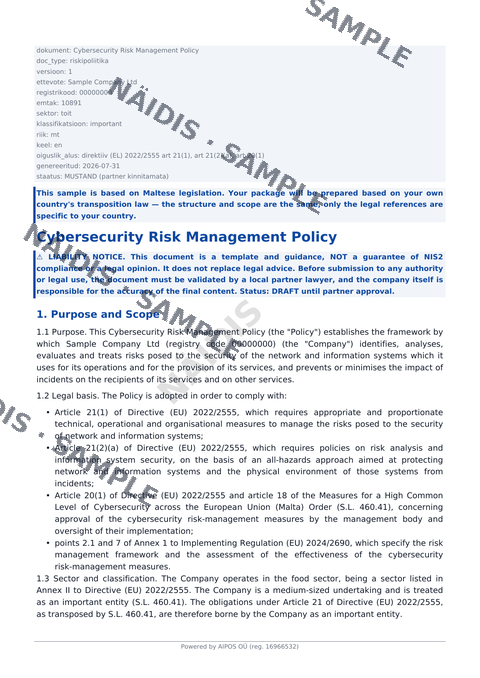 View sample Free sample package before you decide
Loading questions…
NIS2 applicability check: methodology
NIS2 applicability check: sample report
Start the free check 20 questions on the Article 21(2) measures — see instantly where the gaps are.
Free external security check — your domain's security picture in one minute
Check in three minutes whether NIS2 applies to you
The NIS2 document package is usually ready within an hour of payment — we'll notify you when it's done.
Maintenance (monthly) — document re-sign under the law in force
Choose your package:
All prices are net (excluding VAT). Invoices are issued by AIPOS OÜ (Estonia).
NIS2 Document Package — Malta
299 EUR
Suits a company that is subject to NIS2 and needs all core documents at once: the risk management policy, incident handling plan, business continuity plan, supply chain policy and management documents.
The package includes:
- Cybersecurity Risk Management Policy
- Incident Handling Plan
- Business Continuity Plan
- Supply Chain Security Policy
- Management Responsibility Statement and Training Framework
- Fill-in assistant in the portal
The NIS2 document package is usually ready within an hour of payment — we'll notify you when it's done.
NIS2 Document Package + technical scan — Malta
590 EUR
Suits a company that, in addition to the document package, needs an external technical check of its public infrastructure and wants its documents regenerated for 12 months whenever the national law changes.
The package includes:
- Cybersecurity Risk Management Policy
- Incident Handling Plan
- Business Continuity Plan
- Supply Chain Security Policy
- Management Responsibility Statement and Training Framework
- Fill-in assistant in the portal
- NIS2 technical security check
- 12 months of updates
The NIS2 document package is usually ready within an hour of payment — we'll notify you when it's done.
For accountants, IT firms and consultants: offer NIS2 documentation to your clients
A tool that takes the manual drafting of NIS2 documents off your desk: if you have many clients, it is a new revenue stream alongside your existing work.
If your clients include companies to which NIS2 (Malta: Measures for a High Common Level of Cybersecurity across the European Union (Malta) Order) applies, you can offer the preparation of NIS2 documentation as your own service, under your own name and at your own price.
Add your client list and a first screening shows which of your clients are likely to need a NIS2 service; the final assessment follows after additional questions.
Getting started takes about 5 minutes: you create an account and fill in your profile, and the advisor workspace is open.
Suitable for accounting firms, IT and cybersecurity companies, law firms and individual consultants.
The account is free; you pay only for the documentation you order.
What is NIS2 and who does it affect in Malta?
NIS2 is the European Union cybersecurity directive (EU) 2022/2555, transposed in Malta by the Measures for a High Common Level of Cybersecurity across the European Union (Malta) Order (S.L. 460.41). It significantly widens the scope of obligations: energy, transport, healthcare, digital infrastructure, manufacturing, food industry and many other sectors must implement risk management measures and report incidents to the Critical Infrastructure Protection Department (CIP Department) (Critical Infrastructure Protection Department).
The deadlines are strict: a significant incident requires an early warning within 24 hours, a full notification within 72 hours and a final report within one month. Non-compliance can cost an essential entity up to 10 million euros or 2% of worldwide turnover, and an important entity up to 7 million euros or 1.4%.
Our portal turns NIS2 requirements into practice: the free applicability check shows whether NIS2 applies to your company, and the document package is generated automatically, grounded in the officially applicable law text for your country. Start with the check — it takes three minutes.
How quickly can we get the NIS2 documents?
The free applicability check takes about three minutes. The full NIS2 document package is usually generated within an hour of payment — not in days or weeks.
The complete NIS2 guide — Malta →
NIS2 transposition status by EU country →
NIS2 incident reporting deadlines by EU country →
How the NIS2 measures compare with other frameworks →
NIS2 administrative fines by country →
NIS2 management body training obligation →
NIS2 glossary of legal terms →
NIS2 entity categories — Malta →
The results are an indicative assessment, not legal advice. Your company remains responsible for the final content of any document.
NIS2 — complete overview of the law: Malta
What does NIS2 require in Malta?
In Malta, NIS2 obligations are laid down by S.L. 460.41; the cybersecurity risk-management measures are set out in article 19. The law covers 18 sectors and divides entities into the following classes: essential entity / important entity. The early warning of a significant incident must be submitted within twenty-four (24) hours. The maximum administrative fine is up to 10 000 000 EUR.
NIS2 sectors — Malta
The law applies to 18 sectors, including: Energy, Transport, Banking, Financial Market, Health, Drinking water.
Reference: S.L. 460.41, First Schedule, Second Schedule — View official source
NIS2 entity categories — Malta
- essential entity (article 4)
- important entity (article 4)
shall be considered to be essential entities: (a) entities of a type indicated in the First Schedule which exceed the ceilings for medium-sized enterprises provided for in accordance with Article 2(1) of the Annex to the Commission Recommendation 2003/361/EC; (b) qualified trust service providers and top-level domainReference: S.L. 460.41, article 4 — View official source
Deadlines under national law: Malta
- Early warning: twenty-four (24) hours — early warning
- Incident notification: seventy-two (72) hours — incident notification
- Final report: one (1) month — final report
within twenty-four (24) hours of becoming aware of the significant incident, an early warning, which where applicable, shall indicate whether the significant incident is suspected of being caused by unlawful or malicious acts or could have a cross- border impact; (b) without undue delay and in any event withinReference: S.L. 460.41, article 20 — View official source
Fine levels under national law: Malta
Essential entity: 10 000 000 EUR
When they infringe articles 19 or 20, essential entities are subject, in accordance with sub-articles (1) and (2), to administrative penalties of a maximum of ten million euro (€10 000 000), or of a maximum of two percent (2%) of the total worldwide annual turnover in the preceding financial year of the undertaking to which the essential entity belongs, whichever is higher.Reference: S.L. 460.41, article 32 — View official source
Security measures in the country's own law: Malta
The list of security-measure obligations in the national law contains 10 points.
cybersecurity risk-management measures
(2) The measures in sub-article (1) shall be based on an all- hazards approach that aims to protect network and information systems and the physical environment of those systems from incidents, and shall include at least the following:Reference: S.L. 460.41, article 19 — View official source
Start the free applicability check
View sample Free sample package before you decide